Spotting an email scam used to come with familiar advice: look for spelling mistakes, awkward sentences, and messages that sound a little off. Those clues can still help, but they are no longer enough. Criminals can use artificial intelligence to write convincing messages and correct the language errors that might otherwise give them away. The FBI has warned that these tools are making fraudulent messages more believable and easier to produce.
For businesses, the danger often arrives looking like an ordinary part of the workday. A vendor sends an invoice, a manager requests a purchase, or an account notification asks you to confirm some information. Scammers imitate these routine interactions because the requests can seem reasonable at first glance.
You cannot prove that every email is safe just by looking at it. However, these five warning signs can help you recognize when to stop and verify before taking action.
- The sender’s details do not match who they claim to be.
A familiar display name does not establish who actually sent an email. Expand the sender’s information and examine the full email address, especially the domain after the @ symbol. Watch for substituted letters, extra characters, or an unfamiliar domain attached to the name of a company you recognize. Criminals use these small differences to make impersonation attempts look legitimate.
Compare the address with contact information you already trust rather than relying on the signature in the message. However, even a correct address is not a guarantee of safety. Criminals can compromise genuine business email accounts and use existing conversations to make fraudulent requests seem credible. Treat the sender check as one precaution, not permission to stop checking.
- The message pressures you to act before you can think.
An email threatening immediate account suspension or demanding an urgent payment deserves extra scrutiny. Scammers use urgency, fear, and intimidation to push people into acting before they investigate. The message may sound authoritative and professional while still trying to rush you into a bad decision.
Be particularly cautious when the sender discourages you from checking with anyone else. In one impersonation scheme documented by the FBI, fraudulent invoices instructed recipients to request payment instructions by email rather than telephone, helping the scammers avoid independent verification. A request that makes it harder to confirm the facts should give you a reason to pause.
- The email sends you somewhere unexpected through a link, attachment, or QR code.
A document-sharing notification or account alert may lead to a fake sign-in page rather than the service it claims to represent. Criminals can copy the appearance of legitimate websites to collect the passwords or financial information people enter. An unexpected attachment also deserves scrutiny, even when it is presented as an invoice or another routine business document.
QR codes deserve the same caution as clickable links. The FTC warns that scammers include them in emails and text messages to direct people to fraudulent sites. For an unexpected account notice, open the service through a trusted bookmark or its official app instead of following the message’s instructions. Confirm an unexpected document with the sender through a separate, trusted contact method before opening it.
- The sender wants your password, sign-in code, or sensitive business information.
A message claiming to come from technical support may sound helpful while asking you to hand over account access. Requests to reply with your password should be treated as a serious warning. Employees should not send passwords or sensitive information by email simply because a message appears to come from a manager or another trusted person.
Be just as protective of one-time sign-in codes. Scammers may claim they need a code to investigate suspicious activity or fix an account problem, when their actual goal is to access the account themselves. Do not send someone a code used to authorize your login. Contact your IT provider or the relevant organization through an established channel to verify the request.
- The request changes a normal business process, especially where money is involved.
An email does not need a malicious link or attachment to cause damage. A convincing request to send a legitimate payment to a different account can be enough. Be cautious when a vendor suddenly changes banking details, a manager requests an unusual purchase, or someone asks you to bypass the usual payment approval process. These are situations associated with business email compromise scams.
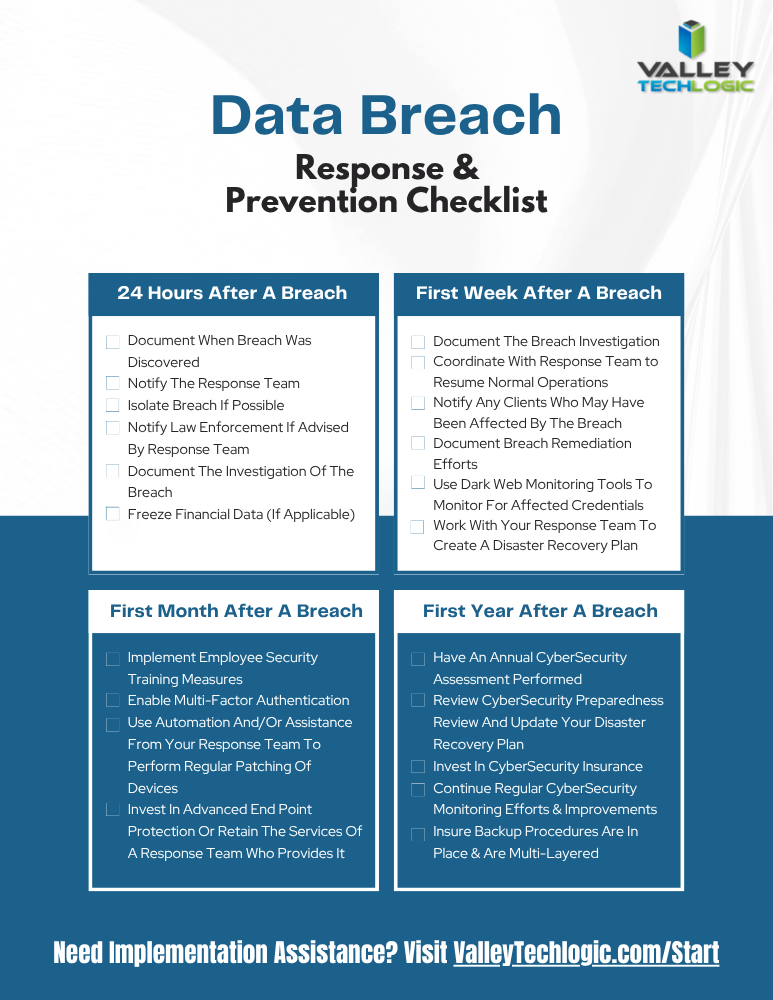
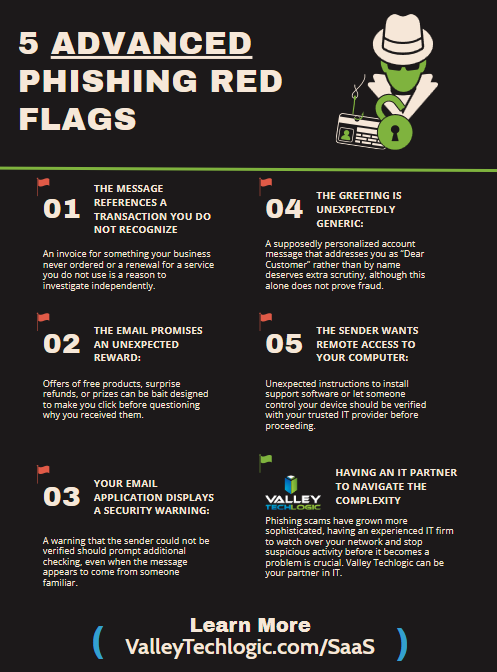
Verify changes to payment instructions by calling a number already in your records, not a new number supplied in the email. Keep any required second approval in place, even when the request appears to come from someone senior. An existing email conversation should not replace independent confirmation when the destination of your money changes. We also have this free resource with five more items to look out for when it comes to phishing scams:
Recognizing suspicious emails should be a shared business practice, not a test employees are expected to pass without support. Give your team a clear process for checking unusual requests and reporting concerns. Regular training and an incident response plan help turn that expectation into something people can actually follow.
At Valley Techlogic, we help businesses strengthen their defenses with email and phishing protection, employee security awareness training, simulated phishing exercises, endpoint protection, and ongoing security monitoring. These services combine technical safeguards with practical preparation for the people using your systems every day.
Your employees should not have to make every security decision alone. Reach out to us today to discuss your current protections and how we can help your business reduce its exposure to phishing and other online scams.
- Meta announced Muse and OpenAI announced Dots, are cutesy avatars the way to mass market appeal with real world application or a cheap gimmick?
- 6 Reasons to restrict admin access to company devices
- Is the AI threat overblown? Why OpenAI, Anthropic and more are cautioning we need to “slow down” on AI innovation and focus on safety
- ChatGPT’s Astra (GPT-6) has been released, is it worth the hype?
- Microsoft is retiring voice and SMS verification in favor of passkeys for Entra users starting February 2027, we tell you how to set this up NOW before you lose access
This article was powered by Valley Techlogic, leading provider of trouble free IT services for businesses in California including Merced, Fresno, Stockton & More. You can find more information at https://www.valleytechlogic.com/ or on Facebook at https://www.facebook.com/valleytechlogic/ . Follow us on X at https://x.com/valleytechlogic